avday
A claim that more than 70,000 Coinbase users were caught in a data breach spread on X on Tuesday 27 October, before Coinbase had said anything. Coinbase says it’s false.
The figure is close to the 69,461 people hit by Coinbase’s breach in May 2025. A Coinbase spokesperson told Unchained they believed the number started with Grok, the AI chatbot on X, conflating the new incident with Coinbase’s May 2025 case.
What did happen is smaller. Amplitude, an analytics company Coinbase uses, had a security incident that affected “a small subset” of Coinbase customers, Coinbase said on X. Its spokesperson told Unchained that “contact and limited transaction data were impacted”. Coinbase hasn’t said how many customers.
The data didn’t include “home addresses, or any other information that would allow someone to directly access your account or your funds.” “Coinbase has not had a data breach,” the company’s support account posted on X, as quoted by Unchained and Decrypt. It said customer funds were “not impacted”.
Coinbase phishing: what users should do now
Leaked contact details are what scammers need to pose as a company. Coinbase is contacting affected customers directly, Unchained reported, but hasn’t said whether they should take any steps. In May 2025 it wrote: “Coinbase will never ask for your password, 2FA codes, or for you to transfer assets to a specific or new address, account, vault or wallet.”
- Distrust contact about the incident. Treat any call, text or email “from Coinbase” about it as suspect, and check through the app instead.
- Never move funds to a “safe” wallet someone gives you. Coinbase says it will never call or text you with a new wallet address to move your funds to.
- Use a stronger second factor than text messages if you haven’t, such as a passkey or security key.
Binance gave users the same warning after its $6.3bn hack on 29 October.
Were 70,000 Coinbase users affected?
Coinbase says no, though it hasn’t given its own count. According to Unchained, the number first appeared on Tuesday evening, US time, nearly three hours before Coinbase’s post, from an X account that gave no source. It was repeated by 23pds, who describes himself as a partner at the blockchain security firm SlowMist. Unchained found no report from SlowMist itself.
The Grok explanation is the spokesperson’s belief. Unchained couldn’t verify it. Viral claims like this are worth checking before sharing: our look at whether Anthropic blocked Reverse Engineer Anything found the errors real but the cause older.
How it compares with the 2025 Coinbase data breach
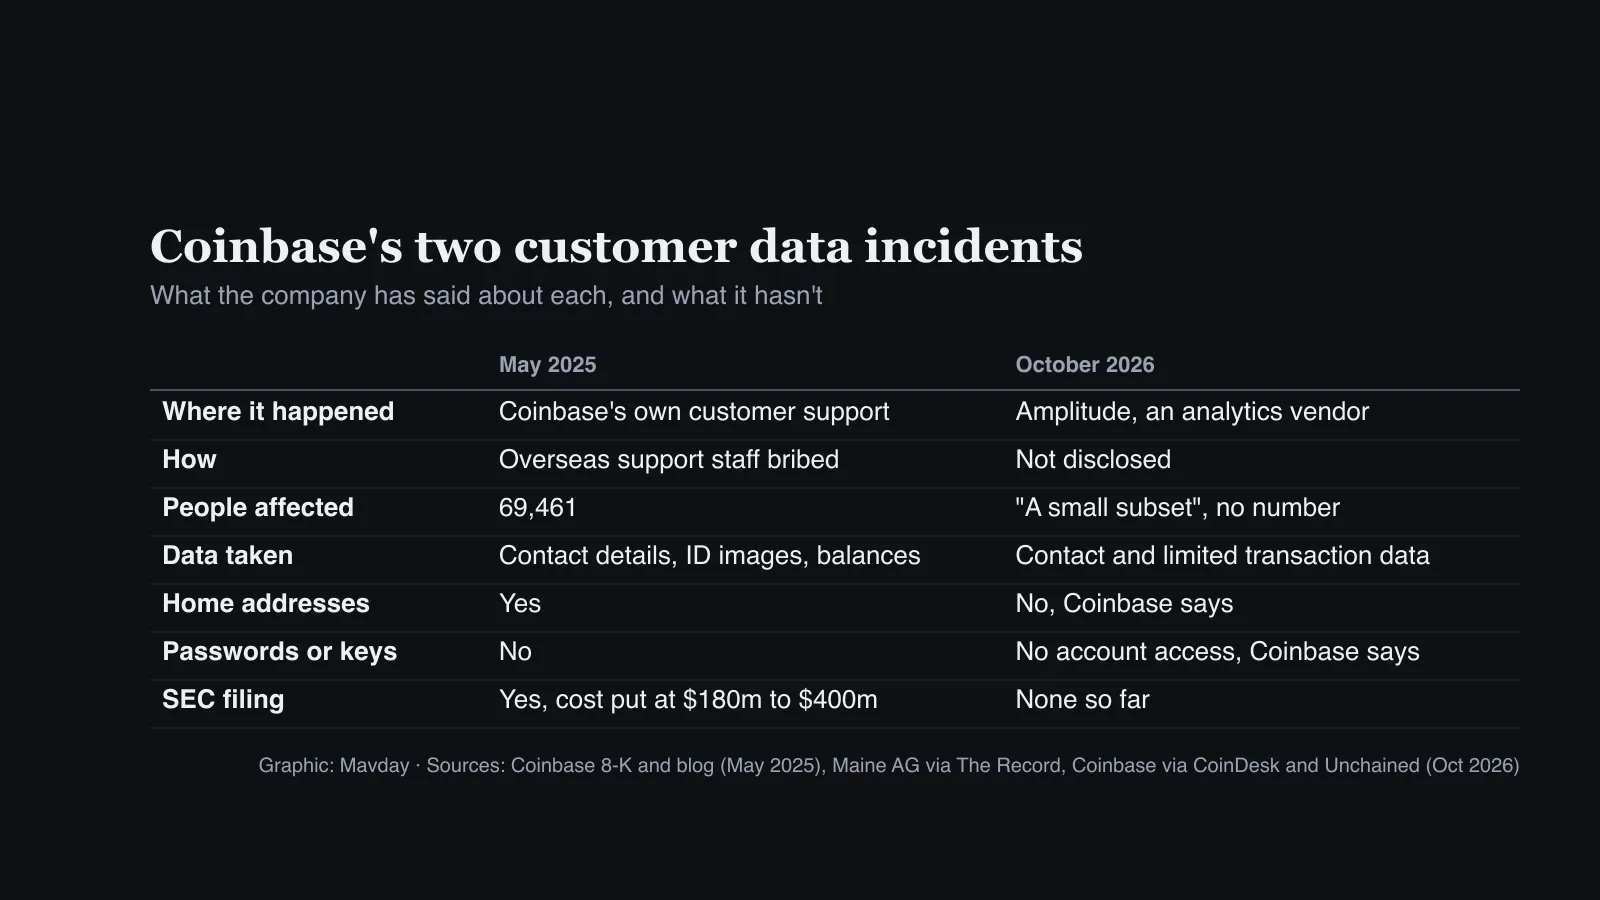
In May 2025, Coinbase said, criminals had paid support staff outside the US for customer data. It refused a $20m ransom demand and put the cost at $180m to $400m. Coinbase isn’t the only finance app hit through a supplier this month: Google Cloud’s London outage disrupted Revolut on 20 October.
What we don’t know yet
- How many customers. Cointelegraph asked and got no reply.
- Which details. Coinbase hasn’t listed the contact fields, or said what “limited transaction data” means.
- Where. Coinbase says it’s telling regulators but hasn’t named them, or said whether UK customers are affected.
- How and when. Neither company has said how the attackers got in, or when. Amplitude didn’t immediately reply to Unchained, and its status page has no notice about the incident.
What happens next
Neither company had filed a form 8-K about the incident with the US Securities and Exchange Commission by 28 October, our search of its EDGAR database found. That’s the form listed companies use for a cyber incident they judge material.
Coinbase reports third-quarter results on Thursday 29 October, after the US market closes, with a live Q&A at 9pm UK time. Amplitude follows on Wednesday 4 November, with a webcast at 10pm UK time. Both are a chance to ask how many customers were affected.